There is a project that boots a computer by asking for twelve words. Type them and the
machine assembles itself — files, contacts, settings, identity. Power it off and it forgets
everything. Its root filesystem lives in memory. Nothing is written to disk, not even the
Wi-Fi password.
It runs on laptops and Raspberry Pis. It does not run on phones. The distance between those
two facts is what interests me here.
It is called n-OS-tr. Those twelve words are a BIP-39 mnemonic, and from it the
system derives every key it needs along the standard NIP-06 path — one index for the user's
identity, another for the admin key of a local relay, a third for a blob store, a fourth for
a mesh node. Preferences and dotfiles live on Nostr relays as replaceable events, encrypted
to yourself under NIP-44, and get projected into the home directory at boot. As of today the
identity layer is still in design; the mesh daemon, the relay and the blob server are
running.
What makes it interesting is not the ephemerality. It is the direction the state travels.
The device as a cache
A normal operating system is its state. Your contacts are a database on your phone. Your
photos are a directory. Your identity, where it exists at all, is an account whose master
copy somebody else holds. Reinstall the system and you have destroyed the machine; restore it
from a backup and you have borrowed one.
In the inverted model the device holds nothing that defines you. The definition sits
elsewhere, signed, and the device is a cache that fills at boot and empties at shutdown. That
reframes what a phone is. It stops being a thing that accumulates your life and becomes a
thing that renders it.
Numbers make this less abstract than it sounds. I measured a follow list off the relay
network myself to see what a piece of a life costs. Measured 28 September 2026: 695 contacts
in one event, 49.9 kilobytes, roughly 74 bytes per person. Same run: a profile carried 675
bytes, an average note about one kilobyte, a long-form article around ten. A timeline of five
hundred notes — an afternoon of scrolling — came to 591 kilobytes.
An entire social graph, the asset platforms treat as their crown jewel, is smaller than one
photograph.
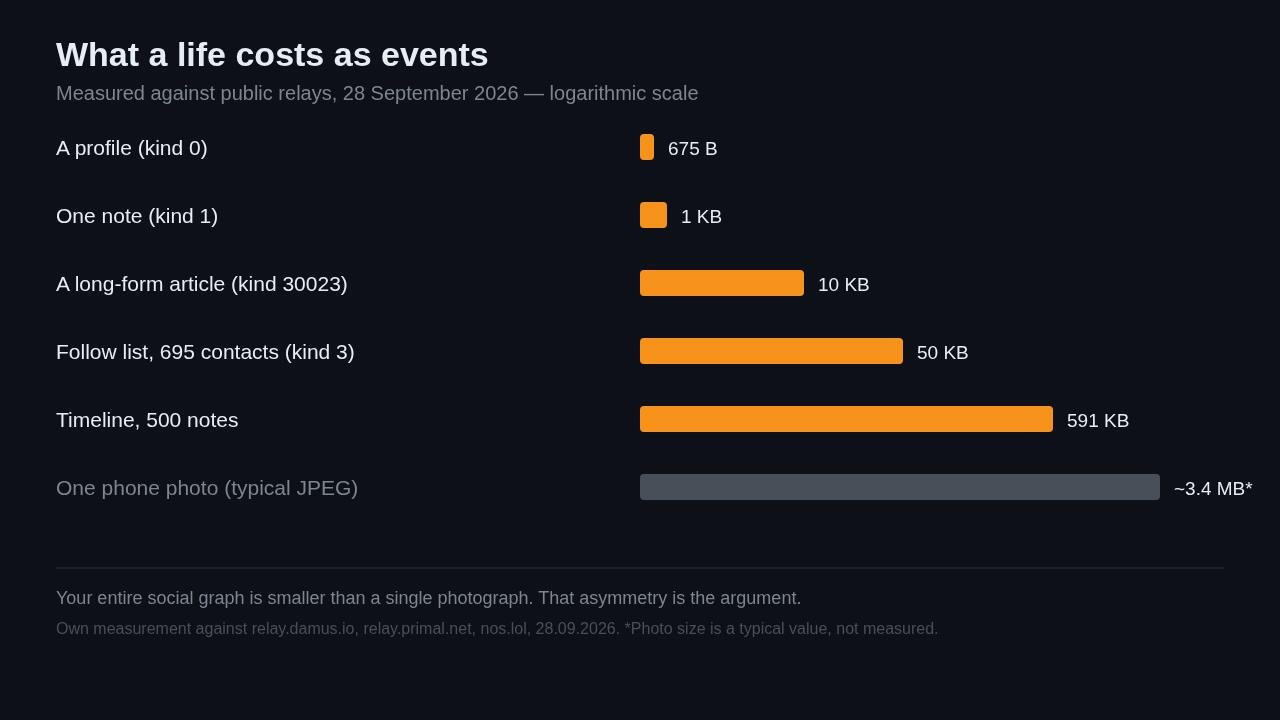
That asymmetry carries the argument. That state — the part that makes you you, in the sense a platform
cares about, is tiny, cheap and portable. What is genuinely large — photographs,
video, the actual megabytes — is also the state nobody needs to hold on your behalf.
What already exists
None of this requires a new operating system to be worth talking about today. The stack is
real and it runs on hardware you can buy.
GrapheneOS is a hardened Android that strips Google out of the base and sandboxes Play
Services when an app insists on them. It runs only on Pixel devices, and the reason is not
laziness: Pixels are the only phones with unlockable bootloaders that still support proper
verified boot after you flash something else. The irony — the most Google-free handset is a
Google phone — is a hardware constraint, not a preference. Motorola announced a partnership
at MWC 2026, with first models expected in 2027.
On top of that system, Amber holds the private key in one place and signs for other apps
through NIP-55, so a compromised client can lie to you but cannot steal your identity.
Zapstore publishes applications as Nostr events under NIP-82: the developer signs the
release, the client checks that signature against a public key before installing, and
discovery comes from the people you follow instead of from a ranking system. Citrine runs a
relay on the phone itself, so drafts and bookmarks have a home that answers to you.
That is a coherent stack. It is also still an Android phone with a Google-derived kernel,
Google's permission model, and Google's release cadence. In 2026 Google moved AOSP source
publication from quarterly to twice a year, Q2 and Q4. That upstream is narrowing while
everyone builds on it.
The part that does not move
Here the idea meets something harder than software.
A phone is not a small computer. It is a radio with a computer attached, and the radio is the
proprietary part. This baseband processor — the chip that talks to the cell network — runs
closed firmware that you cannot audit, cannot replace, and on most devices cannot even
observe. It has direct memory access. It has been the subject of exploitation research for
two decades. Your operating system can be perfectly sovereign and still share a bus with a
component that answers to nobody you can name.
This is why the honest description of a de-Googled phone is reduced dependency, not
eliminated dependency. Its one realistic path to a genuinely open modem is the Quectel
EG25-G inside the PinePhone and PinePhone Pro, and that path is narrow. Modem firmware
updates took years to become routine. Camera support is degraded because most mobile image
signal processors have no mainline driver at all. People building the Linux phone
ecosystem describe their own devices as development targets that enthusiasts run daily —
real, decade-long work, funded thin, with no device supported perfectly.
So the layer where a phone is most exposed is the layer where the Nostr idea has the least to
say. Signing events beautifully does not help you if the component transmitting them is a
black box.
The reachability problem
The second hard part is subtler, and I have not seen it solved anywhere.
A phone's value is that it interrupts you. That is not a side effect of the product; it
is the product. Interruption needs standing infrastructure — something must be watching on
your behalf while your device sleeps, so that the radio can stay off and the battery can
survive until evening.
On Android that watcher is Firebase Cloud Messaging. One party, chosen by the system vendor,
learns when every app wants to reach you and roughly where you are. The de-Googled answer is
UnifiedPush, and it works: ntfy can act as a distributor, it is self-hostable, it can run
entirely inside your own network.
Now look at what you have done. You did not remove the watcher. You became one. Your own
server sees the metadata Google saw — which app is trying to reach you, how often, and when
you are awake. Strictly better if you are the operator. Most people are not. The alternative
is a persistent connection, which means the modem is always on, which is precisely what the
push system existed to avoid.
There is no third option on the table. Interruption requires an intermediary, and the
intermediary learns the shape of your attention. On iOS you do not even get the choice:
Apple's push service is mandatory, which is why the same de-Googled stack cannot be built
there at all.
What it would take
Naming the obstacles is cheap. The interesting question is what the things being missing
actually are, and which of them are missing for technical reasons rather than commercial ones.
Start with the bootloader, because that is where the whole idea either lives or dies. An
unlocked bootloader disables verified boot, and verified boot is what lets a bank app trust
the device it is running on. Open the bootloader and the banking apps, the DRM, the government
ID — all of it stops working, by policy. That is why most manufacturers lock it and why the
lock is not simply corporate malice: a phone that cannot prove what it is running cannot be
trusted with the things people keep on phones.
Fairphone found a way through, and the design is worth naming precisely. They isolate the
radio firmware into a protected section, verified and locked entirely separately from the
Android system. Because a custom ROM never touches the isolated modem code, the manufacturer
can keep the bootloader unlockable without the radio certification falling apart. That is the
trick: separate the part that must stay closed from the part that does not need to be, and
audit them differently. It is not a software feature. It is an architecture decision, made
years before a customer sees the phone.
The second thing that would be needed is carriers willing to allow a device that is not
Android. This is where the practical ceiling shows. A PinePhone running Ubuntu Touch may lack
VoLTE while the same hardware on Sailfish OS gains it — because Jolla licenses proprietary
modem firmware. In the United States it goes further: AT&T blocks non-certified IMEI ranges
outright, and T-Mobile and Verizon want IMS profiles and eSIM provisioning that are rarely
implemented outside Android. A phone that cannot place a call is not a phone, no matter how
well it signs events.
The third is money, and it is the least glamorous. postmarketOS has no device supported
perfectly. Most mobile image signal processors have no mainline driver at all, so the camera
is either missing or reduced to a still-image capture — on more than four in five supported
phones by the project's own account. That is not a hard problem in the sense of being
unsolvable. It is a hard problem in the sense of being unfunded: the maintainers describe
their own work as dependent on free time, and they can name what targeted funding would buy.
And then there is the law, where the finding surprised me.
The EU wrote the problem down. Recital 7 of its smartphone ecodesign regulation states
plainly that "it is currently not possible, or extremely difficult, for the owners of mobile
phones, including smartphones, and tablets to change the operating system of their device,
which is chosen and maintained by the manufacturer". A regulator that names the lock is a
regulator that could open it.
It did not. The regulation mandates five years of operating system upgrades, spare parts
availability for seven years, battery endurance thresholds, and a ban on parts pairing — all
of which make a phone last longer. On the bootloader, the word appears exactly once in the
entire text, and only as one possible place to implement secure erasure of encryption keys.
The right to repair directive, applicable across the EU since 31 July 2026, goes further on
parts and pricing. Neither creates a right to install another operating system, and neither
requires a manufacturer to keep the bootloader unlockable.
Read the recital next to the operative articles and the shape is clear. The EU decided that
phones should last longer, and that the choice of operating system was not its business. It
legislated durability and left sovereignty alone. That is a coherent position. It is also the
reason the sovereign phone is currently an enthusiast project in Europe and a hardware
experiment in China, rather than a product category with a legal floor under it.
What would change it is narrow and specific: a requirement that the bootloader remain
unlockable where a manufacturer's radio isolation already makes it possible, and that devices
which pass certification not be refused by carriers for lacking an Android lineage. Both are
regulatory, not technical. Fairphone has already proved the engineering half. Nobody has
written the other half down.
The identity half has its own missing piece, and it is not cryptographic. Twelve words in a
head are one lost memory away from gone. Steel plate solves storage but not inheritance, and
inheritance is where every self-custody design quietly stops. The workable answer already
exists in the Bitcoin world and has never been ported into an operating system: threshold
recovery, three shares with two needed, held by people who know what they are holding and
survive you. That is a social arrangement wearing a cryptographic coat. It needs no new
protocol — NIP-06 already derives the keys. It needs a default that a person who is not an
engineer will actually follow on the day they set the phone up.
What I could not verify
Two things I could not verify, and I would rather say so than round them off.
One is that a phone which forgets you is a good phone. It is elegant until you are
standing in an airport on a flat battery with a mnemonic in your head. "Carry it in your
head" does not survive a car crash. The answer from that project is that identity is
portable, which is true, and that the device is disposable, which is also true. Neither fact
addresses the thing you have actually done: moved your single point of failure from a device
you can insure to a memory you cannot back up.
The other is the timeline. Every part of the sovereign stack that depends on hardware is
years out, gated by chip vendors with no commercial incentive to open their modems. Every
part that depends on Android is exposed to a narrowing upstream. A confident five-year
prediction would be dishonest. What I can say is that the software half is much further along
than most people assume — identity, signing, distribution are built and running — and that
the hardware half is barely moving.
What the phone is for
Whether a Nostr-based phone can be built is not the interesting question. Much of it has
been. What a phone is for, once you take the idea seriously, is.
A phone is the device that is always with you, always on, always reachable. That is also a
precise description of the device that leaks the most about you. No amount of cryptographic
identity changes the arithmetic: reachability needs a listener, the listener learns
something, and the listener is not you.
Maybe the conclusion is that a phone is the wrong place to insist on sovereignty — that the
sovereign device is the one you leave behind, and the thing you actually carry is not a
machine at all. Twelve words stamped on steel, or held in memory, are more yours than any
handset and they fit in a pocket. Everything else is a cache: warm, useful, and disposable.
Which is the same claim n-OS-tr makes. It just makes it on a laptop, where the radio cannot
argue.